Founder-led, evidence-first.
Work directly with Felix from scope through final review. Prox Offensive is currently a solo practice; any future specialist support will be disclosed in advance and used only with client approval.
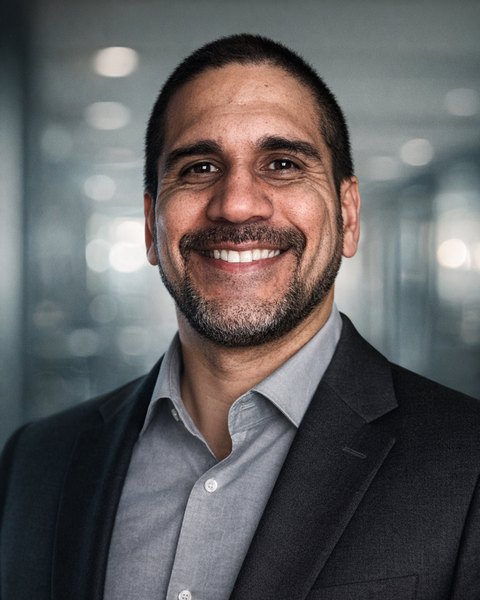
Felix Gutierrez
Founder & Offensive Security Specialist
I'm Felix, offensive security specialist and founder of Prox Offensive Information Security. I help organizations see what attackers see, before the attackers do.
My work centers on external exposure assessment, adversary simulation, and AI-assisted security workflows, backed by open-source tooling I build and publish. I remain responsible for scope, testing, evidence validation, judgment, and the final report.
I'm a member of the Keiser University Sarasota Campus Cybersecurity Department Advisory Board.
Prox Offensive Information Security
 Member of the Lakewood Ranch Business Alliance
I believe in digital sovereignty: knowing exactly what you're exposing, controlling your signal, and building systems that don't require blind trust. Testing starts only after written authorization and stays within the agreed service boundary.
Training & community
Coursework & lab training
- Harvard/edX CS50 — Web Programming with Python & JavaScript (coursework attended; not completed)
- TryHackMe: Completed learning paths — Path to Cyber, Pre Security, Jr Penetration Tester, and Red Teaming
Security community
- Volunteer — BSides St. Pete, BSides Orlando, HackSpaceCon, and HackRedCon
- Participant — HackMiami and BSides Tampa
I stay connected to the security community through conferences and events, and bring those ideas back into my labs, research, and service development.
Research & open source
I run a dedicated research effort: LLM adversarial-robustness testing, multi-agent AI security tooling, adversary-emulation case studies (including APT33), and reconnaissance automation, all published in the open on github.com/DonTrabajo.
This research informs service design: studying how attackers view a public attack surface sharpens the assessment method. Public lab work remains separate from client evidence, and research artifacts are never presented as completed client outcomes.
AI Red-Team Lab
A reproducible adversarial test harness covering prompt injection, data leakage, tool misuse, and other LLM security failure modes.
DonTrabajo/ai-redteam-labProx Recon
Offline-first reconnaissance core: linPEAS parsing and CVE matching, with CI-enforced OPSEC gates. The public core of our recon tooling.
DonTrabajo/prox-reconAI Multi-Agent Lab
Local-first multi-agent red-team lab: orchestration, LLM routing, and OPSEC-first workflows. Sanitized architecture and demos.
DonTrabajo/ProxOffensive-AI-MultiAgent-LabAPT33 Case Study
Adversary-emulation case study with detections, threat-hunting queries, and results/tuning notes.
DonTrabajo/apt33-scythe-case-studyRecon Audit Sample
A public-safe external-exposure audit: methodology, report structure, and a full example report.
DonTrabajo/recon-audit-sampleTry the free DIY Recon Toolkit, or browse everything on GitHub.
How I work
Authorized & ethical
Every engagement requires written authorization. No testing without explicit owner permission.
Evidence-based
Confirmed findings include supporting evidence such as screenshots, requests, and reproducible steps.
Business-context first
We translate technical exposure into impact your leadership and auditors actually understand.
Remediation-focused
Reports prioritize remediation and include verification guidance where it fits the scope.
Want a clear view of your exposure?
Book a short call, tell us what you're running, and we'll scope the right engagement.